
Roles & Permissions
A Role is a set of Permissions a Team Member has access to. There are both default Roles, which can not be edited, and Custom Roles. To change a default Role, clone it into a Custom Role. Custom Roles need the Professional or Enterprise plan. To create one, a Team Member needs the 'Manage Roles' permission.
Default Roles
The default roles that come with every account are 'Admin User', 'Super User', 'Scheduled Call User', 'Volunteer User', 'Internal Communications', 'Website Manager', and 'Email Manager'. These Roles define a variety of common permission sets that an organization may need. 'Admin User' can use every permission. 'Super User' can manage people, events, phonebanks, textbanks, blasts, the team, and roles, but it cannot delete, bulk update, or export people, or manage billing.
You can see the Permissions that each Role has access to by visiting the Roles & Permissions section under Settings, and clicking on the Role. The Roles & Permissions page lists only the roles that you could assign.
Custom Roles
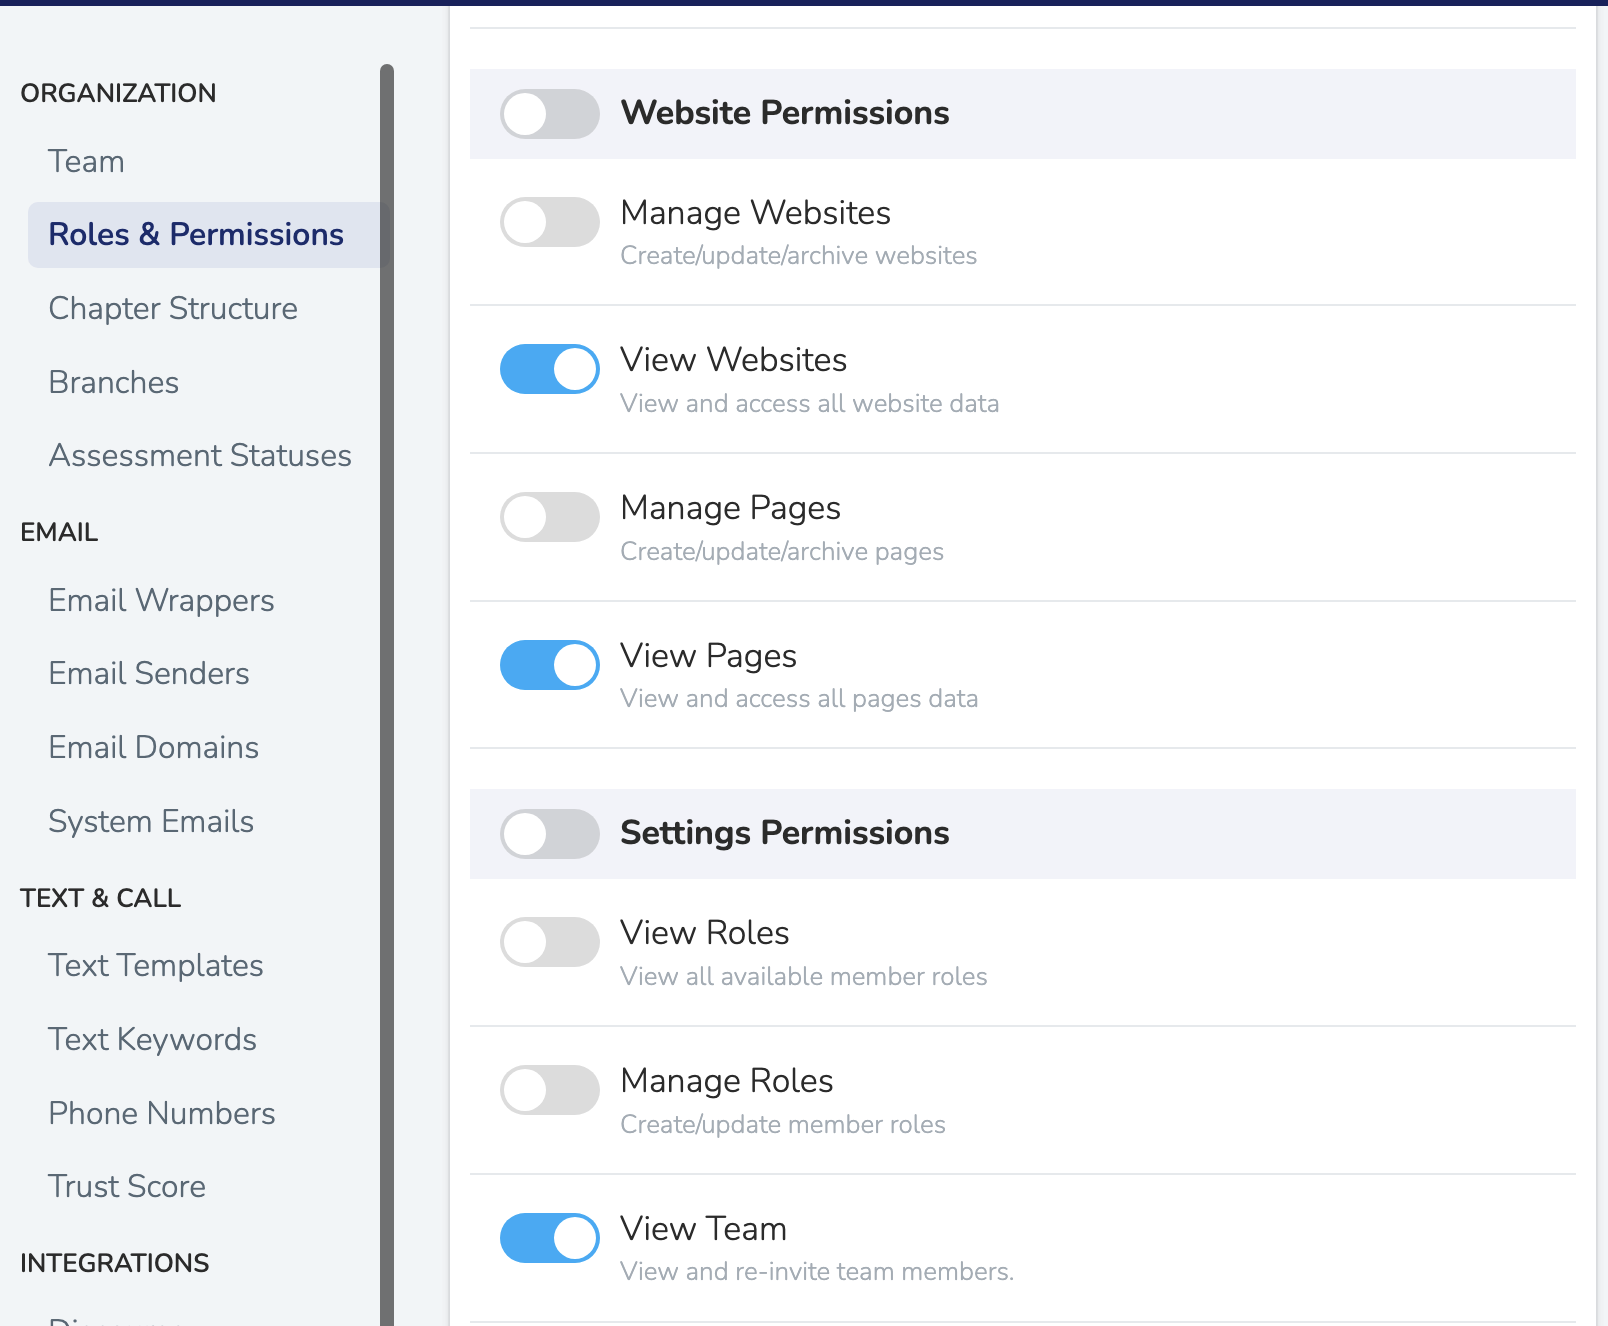
On the Professional plan, team members with the 'Manage Roles' permission can create custom roles to match precise permission sets. On Settings > Roles & Permissions, click 'New role'. Enter a 'Role Name', click 'Create role', and turn on the permissions you want to grant.
Cloning a Role
If you want to create a new role that is similar to an existing one, you can clone it rather than building from scratch. Cloning copies all of the existing role's permissions into a new, fully editable custom role.
To clone a role:
- Navigate to Settings → Roles & Permissions
- Click on the role you want to copy
- Click the Clone Role link near the bottom of the page
- Enter a name for the new role and click Clone Role
The new role appears immediately and can be edited like any other custom role. Cloning needs the Professional or Enterprise plan and the 'Manage Roles' permission. Unless you have the 'Admin User' role or are the account owner, you must hold every permission in the role that you clone.
Tip: Cloning is useful when you need a role that is nearly identical to an existing one but with one or two permissions added or removed — for example, a version of your standard organizer role that also includes the ability to send email blasts.
Common Permission Scenarios
| Scenario | Permission Needed |
|---|---|
| Draft emails/texts but not send them | Enable "Draft" permissions, disable "Send" permissions |
| Send emails/texts | 'Send Email Blasts' alone lets a team member draft and send email blasts. 'Send Text Blasts' alone does the same for text blasts. |
| View contacts but not edit | Enable 'View, Text, and Call All People'. Turn off every permission that adds, updates, merges, imports, or deletes people. |
| Take event attendance | Enable "Manage Events" permission |
| Run phonebanks only | Assign the 'Volunteer User' role. Then add the person on the phonebank's 'Team' or 'Team + Assignments' tab, or share the phonebank's magic link. |
| Create new people or event tags | 'Add New Tags' lets a team member create new people tags, event tags, and follow-up task tags. |
| View protected contact fields (phone, email, address) | Enable 'View Protected Properties'. It also shows restricted custom properties and notes. See Protected Core Fields |
| View and submit 10DLC brand registration and campaign verification | Enable "Manage 10DLC Compliance" permission |
| Log into the dashboard as another team member within your scope | Enable "Impersonate Team Members" permission |
| Allow a team member to connect an AI assistant (Claude, ChatGPT, Cursor) | Enable 'Connect AI Assistants (MCP)'. A connection also needs the Professional or Enterprise plan and the root organization's 'AI Assistant Access (MCP)' setting on 'Enabled' or 'Read only'. |
| Allow a connected AI assistant to add notes, edit tags/properties, save lists, or schedule tasks | Enable "AI Assistant Write Access" permission |
Tip: If someone says "I can't send my email blast," check their role's permissions first. They may have been granted draft permissions but not send permissions.
Impersonating Team Members
Team members with the 'Impersonate Team Members' permission or the 'Admin User' role can log into the dashboard as another team member within their scope. See Team Members for the steps.
Important: All actions taken while impersonating are attributed to the team member being impersonated, not the person who initiated the impersonation session. Use this permission with care and only grant it to trusted administrators.
AI Assistant Permissions
Two permissions control how Team Members can use AI assistants (such as Claude, ChatGPT, and Cursor) with Solidarity Tech:
- Connect AI Assistants (MCP) — Allows this Team Member to authorize an external AI assistant to access Solidarity Tech on their behalf. The assistant can only see what this person's Role can see in the dashboard. This permission is required before a Team Member can connect any AI assistant.
- AI Assistant Write Access — Allows this Team Member's connected AI assistants to make changes, including creating notes, editing tags and custom properties, saving lists, and scheduling follow-up tasks. Without this permission, connected assistants are read-only.
Note: Both permissions work together with the organization-wide AI assistant setting. Even if a team member has these permissions, the root organization's 'AI Assistant Access (MCP)' setting controls connections, and its default is 'Disabled'. Only a team member with 'Manage All Third-Party Integrations' and 'Manage Chapter Structure' at the root organization can change it. See Settings → Chapter Structure on the root organization page.
Updated 20 days ago